Cyber Maturity Assessment
Measure, improveand protect.
Assess your organisation’s cyber capabilities, identify the gaps and get a clear roadmap to strengthen your security posture.

Understanding Cyber Maturity Assessment
A clear measure of your security, and a roadmap to improve it.
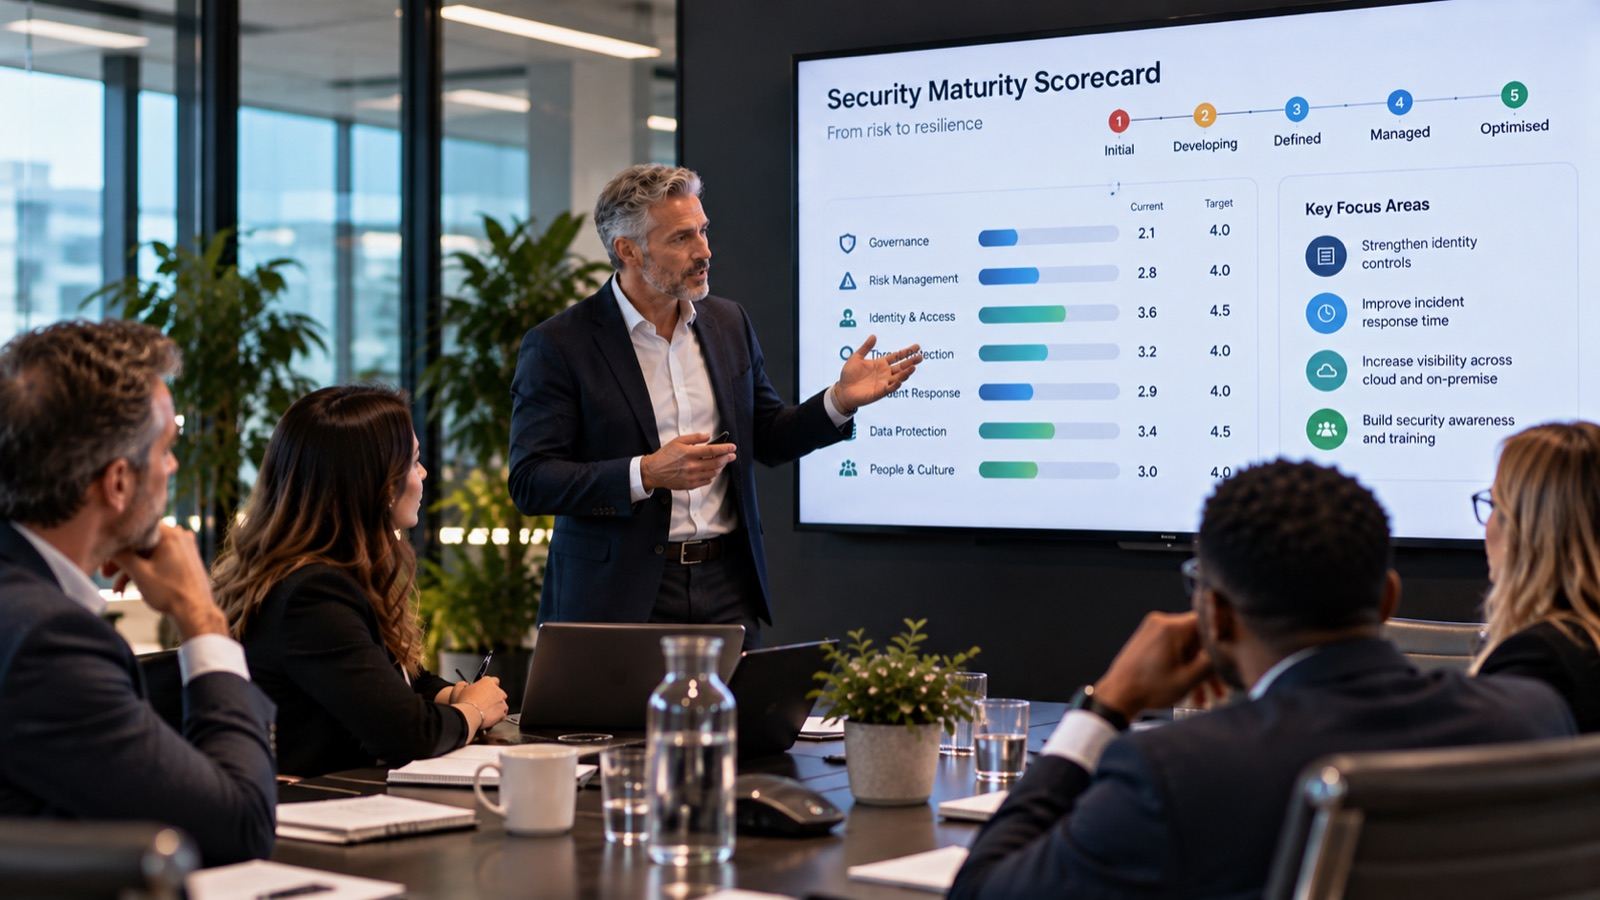
A structured evaluation of your people, processes, governance and technology. We benchmark you against recognised frameworks such as ISO 27001, NIST and NIS2 through interviews, surveys, technical audits and board-level workshops.
Why it matters: it doesn’t just tick a box. It shows where your critical gaps are, helps you prioritise investment and gives you a strategic roadmap to reduce risk and support your business objectives.

Features
Everything you needto plan with confidence.
Six reasons organisations use a maturity assessment to guide their security strategy.

Holistic view
Assess people, processes and technology in one integrated review.

Gaps & priorities
Focus resources on the areas of greatest risk or impact.

Compliance & governance
Align with ISO 27001, NIS2, GDPR and other regulatory frameworks.

Industry benchmarking
Compare your maturity with peers and best practice.

Strategic investment
Direct budget and resources to high-value security improvements.

Board engagement
Clear insights that support informed executive decisions.
The challenges it solves
Technology aloneisn’t enough.
Many organisations invest heavily in tools but lack visibility of readiness, governance and process. The assessment uncovers gaps like these.
01
Untested incident response
Plans that are unclear or out of date when an incident hits.
02
Poor policy enforcement
Policies that exist on paper but aren’t followed in practice.
03
Low staff awareness
People who don’t recognise threats or know how to report them.
04
Unmonitored systems
Assets and activity nobody is watching, leaving attacks undetected.
By the numbers
The threatin numbers.
30%
of UK businesses did a cyber risk assessment last year
57%
of medium businesses have a formal cyber security strategy (74% of large)
52%
of small businesses have a cyber security policy, down from 59% a year earlier
The onboarding process
From first conversationto clear roadmap.
Six steps from scoping to a plan you can act on, and keep improving.
01
Discovery & scoping
Define objectives, scope and stakeholders for the assessment.
02
Baseline assessment
Collect data on policies, processes, awareness and technology.
03
Gap analysis
Benchmark findings against industry standards and best practice.
04
Reporting & insights
A detailed report with prioritised actions and a roadmap.
05
Stakeholder review
Present findings to executives, boards and security teams.
06
Continuous improvement
Ongoing monitoring, re-assessment and strategy refinement.

Related services
Strengthen yourprotection further.
Services that help you act on your assessment findings.
vCISO
On-demand cyber security leadership to deliver your roadmap.
Learn more

Attack Surface Management
See and secure every corner of your digital attack surface.
Learn more
Cyber Awareness Training
Turn your people into a strong first line of defence.
Learn more
Board Cyber Crisis Simulation
Prepare your board to lead through a real cyber crisis.
Learn more
Case study
Cyber Maturity Assessmentin action.
Multinational professional services firm
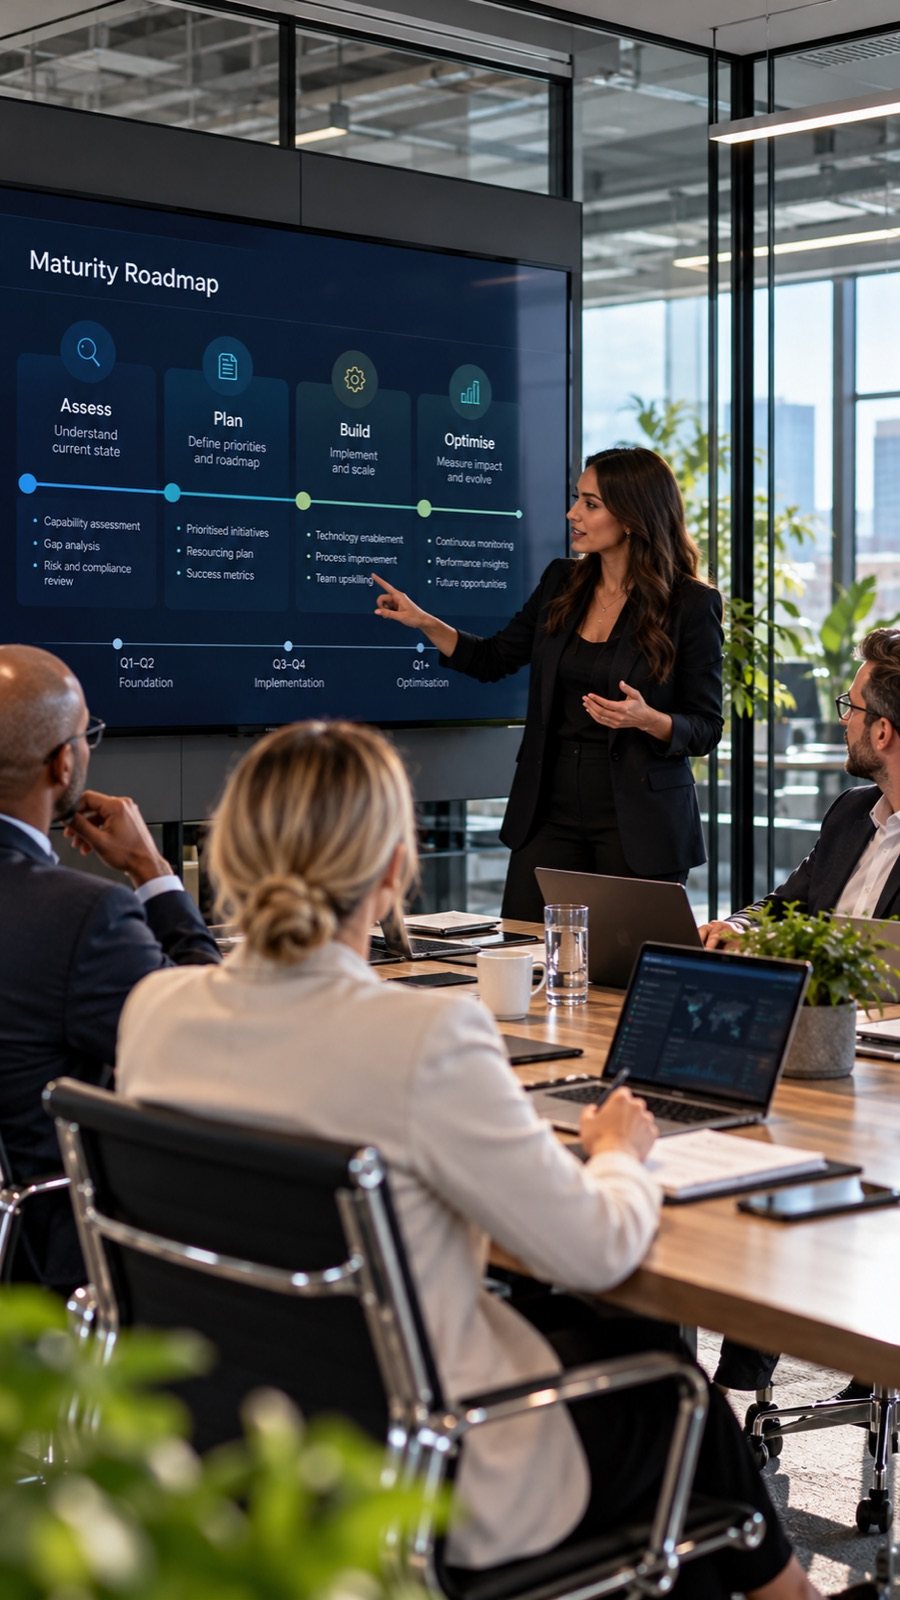
One clear roadmap for cyber maturity across three continents.
Service: Cyber Maturity Assessment
The challenge
The assessment revealed inconsistent policies, uneven staff awareness and gaps in incident response planning across the firm’s regions.
The approach
CyberQ delivered a detailed maturity report with prioritised recommendations and an actionable roadmap.
The result
Within nine months the firm had strengthened governance, improved staff training and closed critical gaps, leading to faster incident response and greater executive confidence.
3
continents assessed against one standard
9 months
to strengthen governance and close critical gaps
AskQ Health Check
How resilient are you, really?
Answer 13 quick questions and get a score across six areas, plus where to focus first. It takes about three minutes.
FAQs
Questions,answered.
What organisations most often ask us about Cyber Maturity Assessment. Can’t find your question? Speak to one of our experts.
View all FAQs
A structured review of your people, processes, governance and technology, benchmarked against frameworks such as ISO 27001, NIST and NIS2, with a prioritised roadmap for improvement.
Through interviews, surveys, technical audits and board-level workshops, so we see how security works in practice, not just on paper.
Recognised frameworks including ISO 27001, NIST and NIS2, aligned to the regulations that apply to you, such as GDPR.
A detailed maturity report with prioritised recommendations and an actionable roadmap, presented to your executives and security team.
Regularly. Ongoing assessments track progress against your roadmap and keep pace with new threats and regulations.
Get started
Talk to us aboutCyber MaturityAssessment.
Book a demo, ask a question or download the service sheet to share with your team. A CyberQ specialist will be in touch.
Download service sheet

Emergency response
Under attack right now? Don’t fill in a form.
Call our incident responders and we’ll help you contain it and recover.
0800 0614 715
Send us a message
Tell us a little about your organisation and what you need. Fields marked * are required.