
Manufacturing
Innovate with confidence.Verify with rigour.
Connecting machines, sensors and the cloud to your ERP makes the factory smarter, and makes the ERP part of your attack surface. CyberQ gives manufacturers the independent assurance to modernise with confidence.
The digital factory
Once the factory is connected, your ERP is part of the attack surface.
Smart CNC machines, IoT sensors and cloud links all feed the ERP, often alongside machinery that has run reliably for decades. Every new connection improves efficiency. Every one is also a bridge: compromise one device and an attacker can reach your financials, formulas and bills of materials.
Cyber security isn’t about slowing digital adoption down. It’s the guardrails that let you modernise safely: security built into every implementation, then checked independently before it goes live. Innovate, then verify.
Key risks
What are youprotecting against?
Digital transformation brings real competitive advantage, but connecting production lines to enterprise and cloud systems redraws the threat landscape. These are the risks we see most often.

Outdated ERP is an open door
Unsupported, on-premise ERP versions and skipped vendor patches leave your most valuable system exposed. Upgrading is a security decision.

Every connection is a bridge
Smart CNC machines, IoT sensors and cloud links all feed the ERP. Compromise one device and an attacker can reach your financials, formulas and bills of materials.

People are the first target
Attackers rarely break through firewalls when they can trick someone into handing over access. AI-written spear phishing, supplier impersonation and invoice fraud now target shop-floor and finance teams.

Legacy controllers and default logins
Old PLC firmware, factory-default industrial credentials and unsegmented shop-floor sensors give attackers an easy first foothold.

Exposed integrations
Exposed API tokens, unencrypted machine-to-machine messaging and unchecked third-party connectors become the path from the shop floor to your core systems.

Ransomware and downtime
When the ERP is encrypted, lines stop, orders slip and recovery can take weeks. Data is often quietly taken first, then used for extortion.
Operational reality
The anatomy of theconnected factory.
Attacks on manufacturers rarely start at the ERP. They start at the edge of the network and move inward, layer by layer.
Layer 01 · Entry point
Edge and machine
Legacy PLC firmware, default industrial credentials and unsegmented shop-floor sensors.
Layer 02 · Transit path
Integration and API
Exposed API tokens, unencrypted machine messaging and unchecked third-party vendor connectors.
Layer 03 · Target asset
Core ERP database
The crown jewels: proprietary formulas, bills of materials, customer banking records and pricing.
Attack path and mitigation
Breaking the lateralmovement chain.
CyberQ helps manufacturers build a layered defence, so an attacker who gets a foothold can’t turn it into a factory-wide incident.
Stage 01
Initial foothold
The risk: attackers exploit unmonitored external gateways and social engineering.
How we mitigate: multi-factor authentication across every service, email security and an awareness programme.
Stage 02
Lateral shift
The risk: flat OT and IT networks let attackers pivot freely from machine to machine.
How we mitigate: micro-segmentation, shop-floor firewall rule testing and continuous vulnerability management.
Stage 03
Privilege creep
The risk: hard-coded credentials on legacy PLCs hand out administrative rights.
How we mitigate: privilege audits and credential penetration testing before go-live.
Stage 04
Data extortion
The risk: unmonitored data theft leads straight to ERP ransomware.
How we mitigate: air-gapped backups and detection of unusual outbound traffic.
Real-world example
Five weeks without production, on our doorstep.
The 2025 attack on Jaguar Land Rover stopped UK production for about five weeks and affected around 5,000 organisations across its supply chain, at a cost to the UK economy of about £1.9 billion. Its Solihull and Wolverhampton plants are a short drive from our Birmingham headquarters.
By the numbers
Manufacturingunder attack.
£1.9bn
cost of the 2025 Jaguar Land Rover attack to the UK economy, the most economically damaging cyber event in UK history
~5,000
organisations affected across the supply chain; UK production stopped for about five weeks
32%
of intrusions start with an exploited vulnerability, the top way in for six years running
Source: Mandiant M-Trends 2026
£241,620
added to a UK breach by supply chain compromise, the largest single cost factor
Our approach
Innovate,then verify.
Don’t hold back on modernising the factory. Build security into every ERP and automation project, then have it checked independently.
01
Keep the platform current
Move off unsupported, on-premise versions and apply vendor patches as routine. Upgrading is a security decision.
Vulnerability Management

02
Map every connection
Every machine, sensor and app linked to the ERP is recorded and reported to the security team, so nothing joins the network unseen.
Attack Surface Management
03
Cyber test before go-live
Like PAT testing a new appliance: every new platform or integration is tested before it touches live data or production networks.
Penetration Testing
04
Separate the build from the check
Your ERP and automation partners build; CyberQ independently assesses. Nobody marks their own homework, and the board stays accountable.
Cyber Maturity Assessment
Continuous assurance
Find it, fix it,prove it.
Vulnerability management keeps known weaknesses under control every day. Penetration testing proves whether your defences hold up against a real attacker.
Vulnerability management: a living cycle
- 01
Discover
Automated discovery of every IP address, controller and cloud endpoint.
- 02
Prioritise
Triage by real exploitability and business impact, not generic severity scores alone.
- 03
Remediate
Targeted coordination with your implementation teams for critical patching.
- 04
Validate
Rescanning and verification, so fixes stay fixed.

Vulnerability scanning
An automated hygiene check for known, catalogued flaws.
- How often
- Continuously, across your networks.
- Think of it as
- Checking every window latch is locked.
- Limitation
- Misses bespoke business-logic flaws.
Penetration testing
The “digital PAT test”: ethical hackers probing ERP custom code, API connectors and machine-to-cloud integrations.
- How often
- Before go-live, then at least once a year.
- Think of it as
- Testing whether the wall holds under pressure.
- You get
- Proven attack paths and verified fixes.
Solutions for manufacturing
Cyber security builtaround your business.
CyberQ combines specialist expertise, technology and continuous protection to address the risks that matter most to manufacturers.
Cyber Maturity Assessment
Benchmark security across business and production environments, with a roadmap that respects uptime.
Learn more
Vulnerability Management
Identify weaknesses across plants, networks and ageing systems, prioritised by operational impact.
Learn more
Penetration Testing
CREST-accredited testing of your networks, applications and remote access, before attackers find the gaps.
Learn more
Managed XDR
24/7 monitoring to detect suspicious activity early, before it can reach production.
Learn more
Configuration Review
Check that firewalls, remote access and network segmentation are set up to keep threats contained.
Learn more
Emergency Readiness & Response
Be ready to isolate, contain and restart safely if an attack hits.
Learn more
Cyber Awareness Training
Build secure habits across engineering, shop-floor and office teams.
Learn more
vCISO
Senior security leadership to align cyber strategy with production, safety and growth plans.
Learn more
Outcomes
What better cyberresilience looks like.
Resilience isn’t about never being attacked. It’s about keeping lines running safely when something does go wrong.
01
Reduce disruption
Minimise the risk of cyber incidents stopping lines or delaying customer orders.
02
Improve visibility
Understand your exposure across business systems, production networks and suppliers.
03
Respond faster
Detect and contain threats before they spread to the factory floor.
04
Protect business continuity
Keep production running safely, and restart quickly if you have to.
Case study
Manufacturingin action.
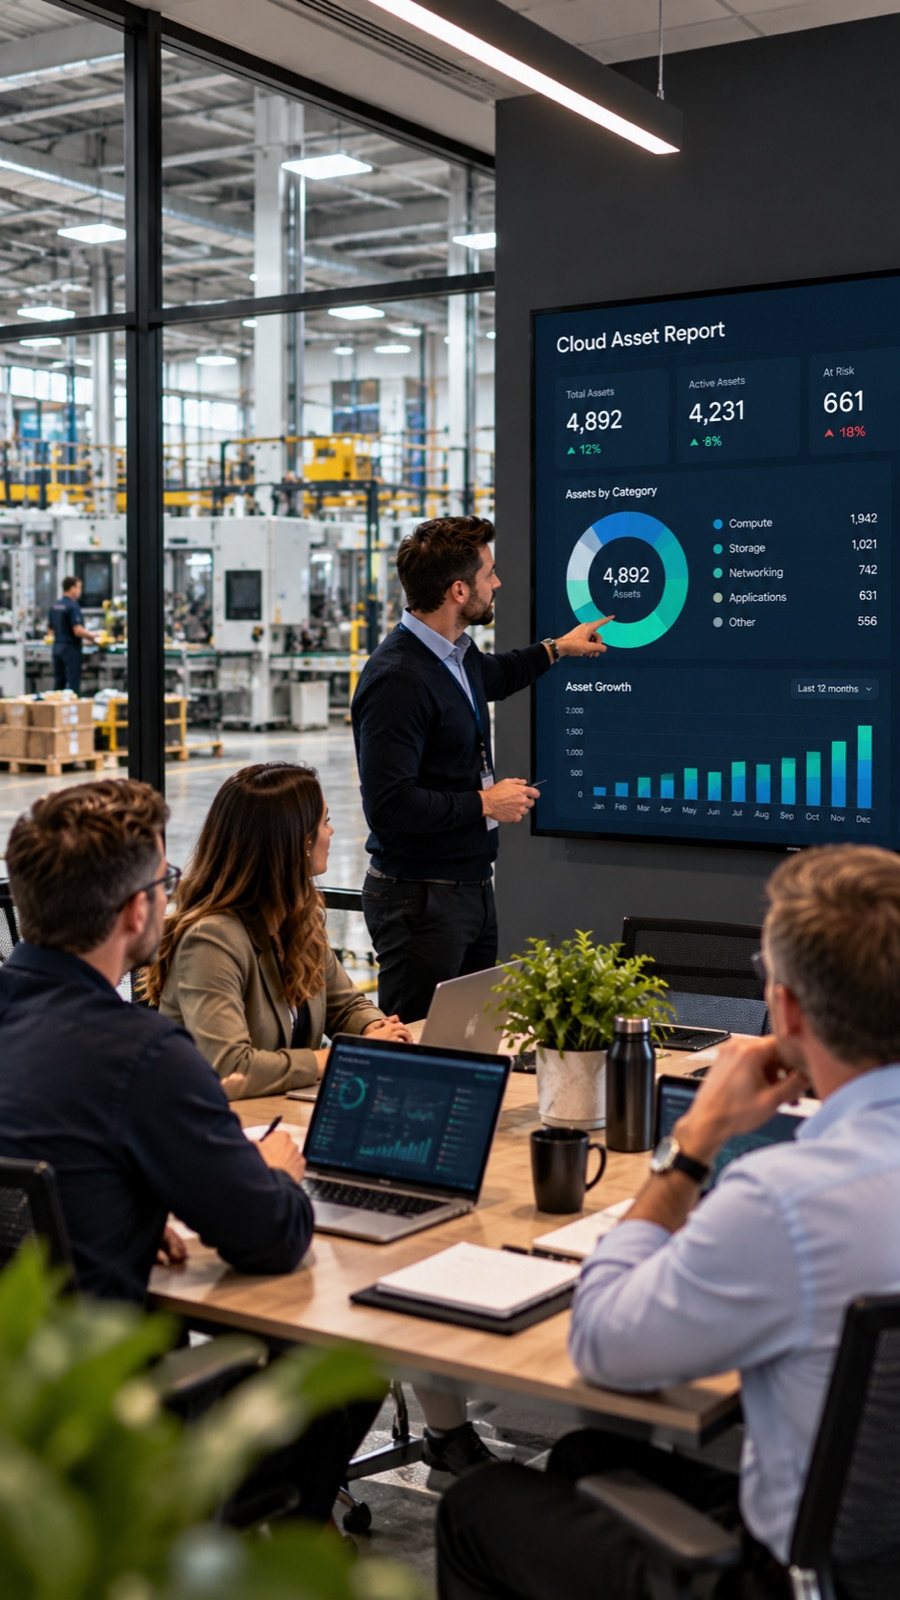
UK-based manufacturing company with international sites
Over 200 unknown resources found, and unknown assets cut by 75% in six months.
Service: Attack Surface Management
The challenge
After moving to multiple cloud providers, the business had no central view of its IT estate and was worried about shadow IT and supply chain exposure.
The approach
CyberQ deployed Attack Surface Management to scan and monitor every digital asset continuously, ranked high-risk issues by business impact, and worked with the internal IT team on remediation.
The result
Within six months, critical cloud misconfigurations were fixed, board reporting improved, and the business could show measurable risk reduction to regulators and insurers.
200+
previously unknown resources found, including misconfigured cloud storage and test environments
75%
reduction in unknown assets within six months
Human Reconnaissance is that extra level of insight and protection that complements our group cyber strategy.
Compliance & regulation
Stay secure.Stay compliant.
Manufacturers face rising expectations from regulators, customers and supply chains. We help you understand which requirements apply, assess where you stand and close the gaps.
IEC 62443
The international series of standards for securing industrial automation and control systems.
NIS2 Directive
EU rules that bring many manufacturing sectors into scope — relevant if you operate in or supply the EU.
ISO/IEC 27001
The international standard for information security management, increasingly requested by customers.
Cyber Essentials
The UK Government-backed baseline, often required by customers and public-sector supply chains.
UK GDPR
Protecting the personal data of employees, customers and suppliers.
Which requirements apply depends on your organisation, where you operate and who you supply. We’ll help you confirm your obligations — this is guidance, not legal advice. CyberQ is itself ISO 27001 and Cyber Essentials certified and CREST accredited.
Executive governance
Three questions everyboard must ask.
Directors are accountable for operational resilience. Independent evidence gives you a defensible answer to each of these.
Question one
“Who validated the integration?”
Make sure independent testing happened before anything connected to the production ERP.
Ask for: test certificates
Question two
“What is our real blast radius?”
Confirm that an infected CNC machine can’t pivot through to your financial records.
Ask for: segmentation audits
Question three
“How stale is our patch cycle?”
Check that firmware and ERP vendor updates are applied proactively, every month.
Ask for: remediation SLAs
Why CyberQ
Why organisationschoose CyberQ.
Independent
Vendor-neutral advice focused on your actual risk, not someone else’s sales target.
Expert
Experienced cyber security specialists who understand business as well as technology.
Globally resilient
24/7 protection, monitoring and response from teams in multiple locations, so cover never depends on a single site.
Business focused
Security designed around resilience, continuity and commercial outcomes.
Insights
Manufacturing cyber securityinsights.
View all articles
-
Cyber security in Birmingham and the West Midlands: a practical guide for local businesses
Read more: Cyber security in Birmingham and the West Midlands: a practical guide for local businesses -
Operational resilience and cyber: what UK financial services firms need to show
Read more: Operational resilience and cyber: what UK financial services firms need to show -
Google Workspace security checklist: 9 settings to review today
Read more: Google Workspace security checklist: 9 settings to review today
Get started
Innovate, then verify.
Talk to us about independent assurance for your next ERP, automation or digital factory project, or find out where your plants are exposed today.
AskQ Health Check
How resilient are you, really?
Answer 13 quick questions and get a score across six areas, plus where to focus first. It takes about three minutes.
FAQs
Questions,answered.
The things organisations most often ask us before getting started. Can’t find what you’re looking for? Browse the full list or speak to one of our experts.
View all FAQs
Still have questions?
Get in touch →Once machines, sensors and cloud services connect to the ERP, it becomes part of the attack surface. An attacker who compromises one connected device can work towards your financials, formulas and bills of materials, so the ERP needs protecting as the crown jewels it is.
It’s a penetration test before go-live. Just as you’d PAT test a new appliance before plugging it in on the shop floor, every new platform or integration should be tested by ethical hackers before it touches live data or production networks.
Independent testing is better practice. Builders test that systems work as expected; independent testers look for how they break. Separating the build from the check removes blind spots and gives your board, insurers and regulators objective evidence.
Book a demo or speak to one of our experts. We’ll learn about your organisation, your current security set-up and your goals, then recommend the right starting point — often a Cyber Maturity Assessment to give you a clear picture of where you stand.
Our Security Operations Centre monitors your environment 24/7/365, investigates suspicious activity and helps your team respond, without the cost of building and staffing your own SOC. Our analysts work from multiple locations, so the service is globally resilient and never depends on a single site.
Yes. CyberQ is CREST accredited, ISO 27001 certified, Cyber Essentials certified and a registered HM Government G-Cloud supplier.
Call our incident responders on 0800 0614 715 straight away rather than filling in a form. Our Emergency Readiness & Response team will help you contain the incident and get back to business.
We protect more than 150 organisations worldwide, with specialist experience in manufacturing, logistics and retail, and support across the UK, Europe, South Africa, the US and Asia.